Logs collected in your network, emails and card numbers masked by default.
Your logs are collected inside your network, and emails and card numbers are masked by default before they reach your GhostAnalyst workspace.
NACSA licensed
Where your data goes, step by step.
Your logs are collected inside your network, and emails and card numbers are masked by default before they reach your GhostAnalyst workspace. Everything after works on cleaned, structured events.
- Step 1Collected on siteThe Sidecar reads your devices inside your own network
- Step 2Cleaned on siteLogs are put into one standard format and emails and card numbers are masked by default
- Step 3Sent encryptedEvents leave over one encrypted outbound connection
- Step 4ExplainedOn-cluster AI returns a verdict with its reasoning
A court can only compel what we hold. Emails and card numbers are masked by default before it reaches us.
Laws such as the US CLOUD Act let authorities order a provider to hand over data it holds, wherever that data is stored.
When a SIEM copies your raw logs to its own cloud, that copy is in reach. With GhostAnalyst, your logs are collected inside your network, and emails and card numbers are masked by default before they reach your GhostAnalyst workspace.
What changes for your team.
| Question | Typical cloud SIEM | GhostAnalyst |
|---|---|---|
| Where do logs go? | Copied to the vendor's cloud | Collected in your network, emails and card numbers masked by default |
| What does the AI see? | Raw events, often with personal data | Your events, with emails, IC, passport and phone numbers, MAC addresses and secrets masked where detected before a hosted model sees them. Best effort. |
| Why was an alert raised? | A rule name and a score | Reasoning in plain words, mapped to MITRE ATT&CK |
| Who acts on it? | Your team, alone | Your team, backed by a licensed SOC |
| How long to go live? | Weeks of setup is common | Under an hour |
Every verdict comes with its reasons.
Your analysts, managers and auditors read the same plain explanation of why something was flagged and what was done.
Explore Mission Control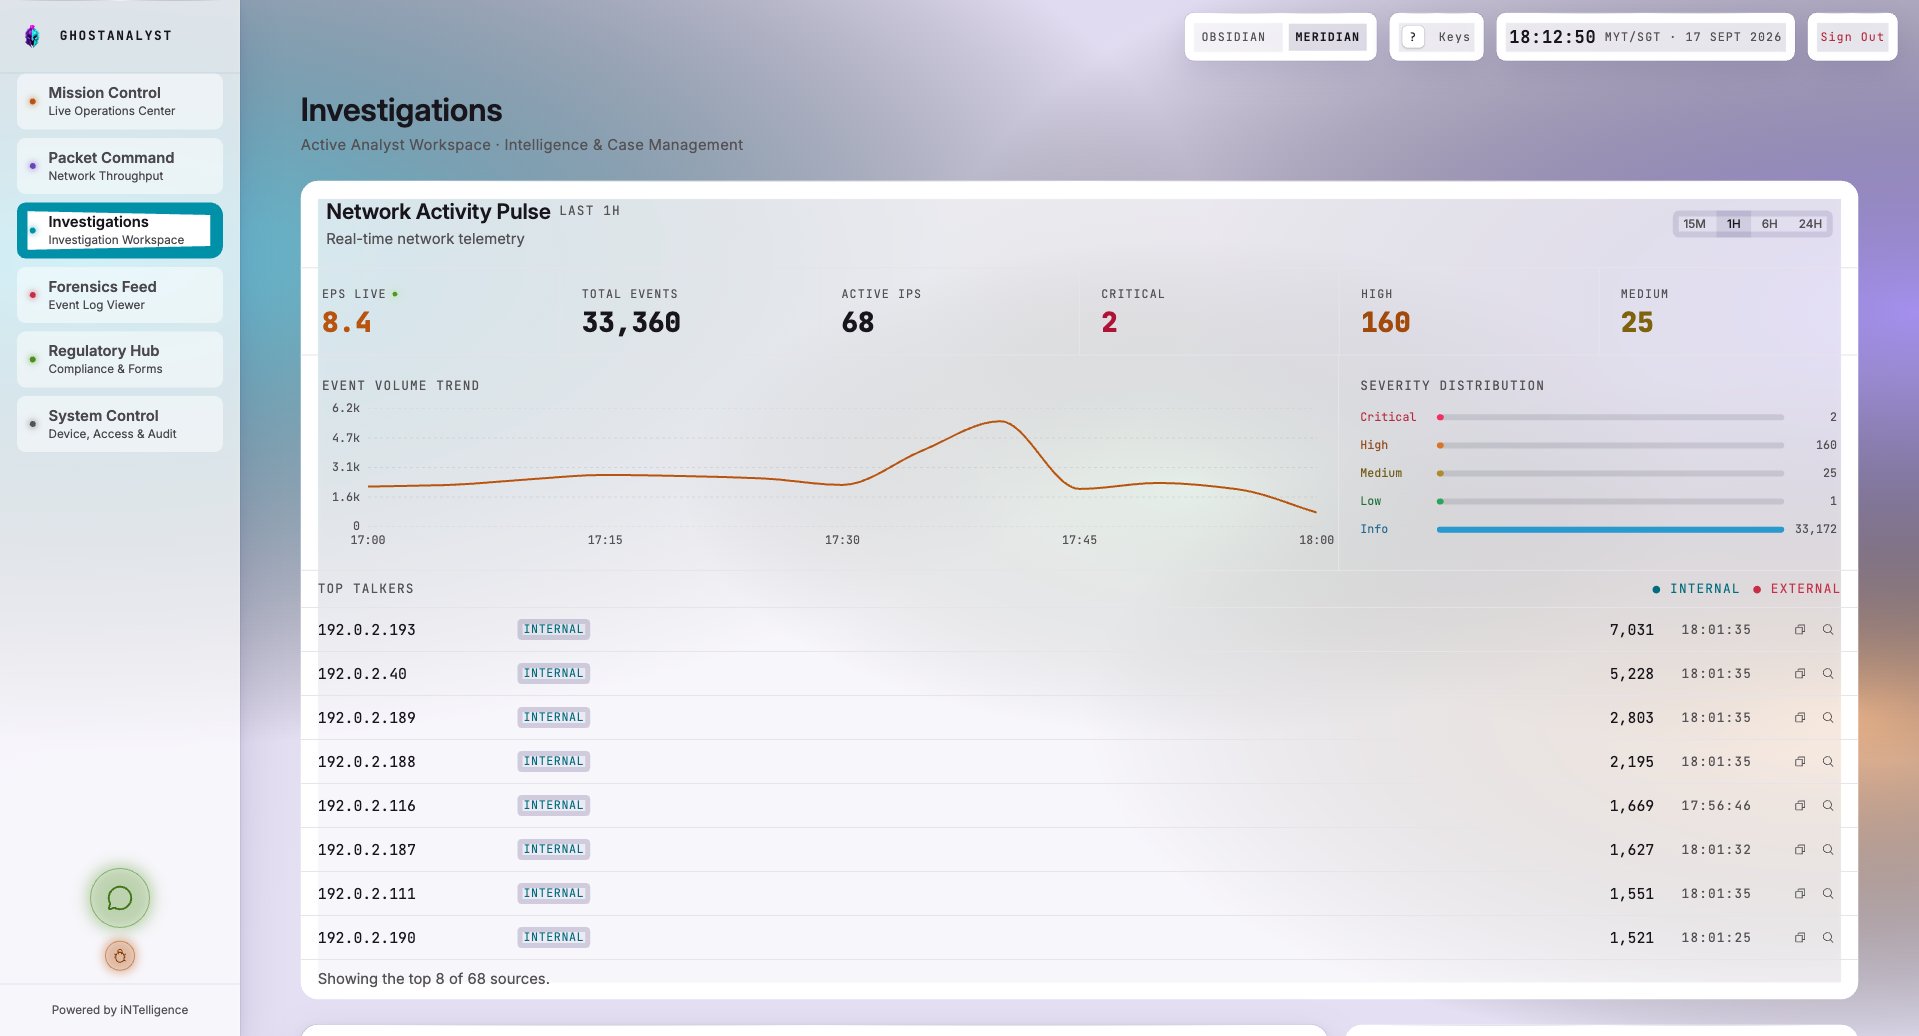
Real numbers from a production deployment, not a demo.
- Sector
- Public service · regulated jurisdiction
- Challenge
- Raw security logs could not leave the country
- Deployment
- Live in under an hour
Three reasons buyers choose us.
A licensed SOC behind the software
Every subscription includes SOC and MDR from a licensed provider, with on-site support.
Try it on your own logs
A 60-day full-platform trial, direct with us. No credit card and no inbound firewall changes.
Start free trial →Bought through partners near you
Authorised partners scope, quote and support your subscription, priced per monitored device.
How pricing works →See it on your own logs.
60-day full-platform trial. No credit card. No inbound firewall changes. Live in under an hour.