Six stages from raw log to a case your team can act on.
Collection and personal-data removal happen on your site. Detection, reasoning and response run on clean, structured events, and every step leaves a record.
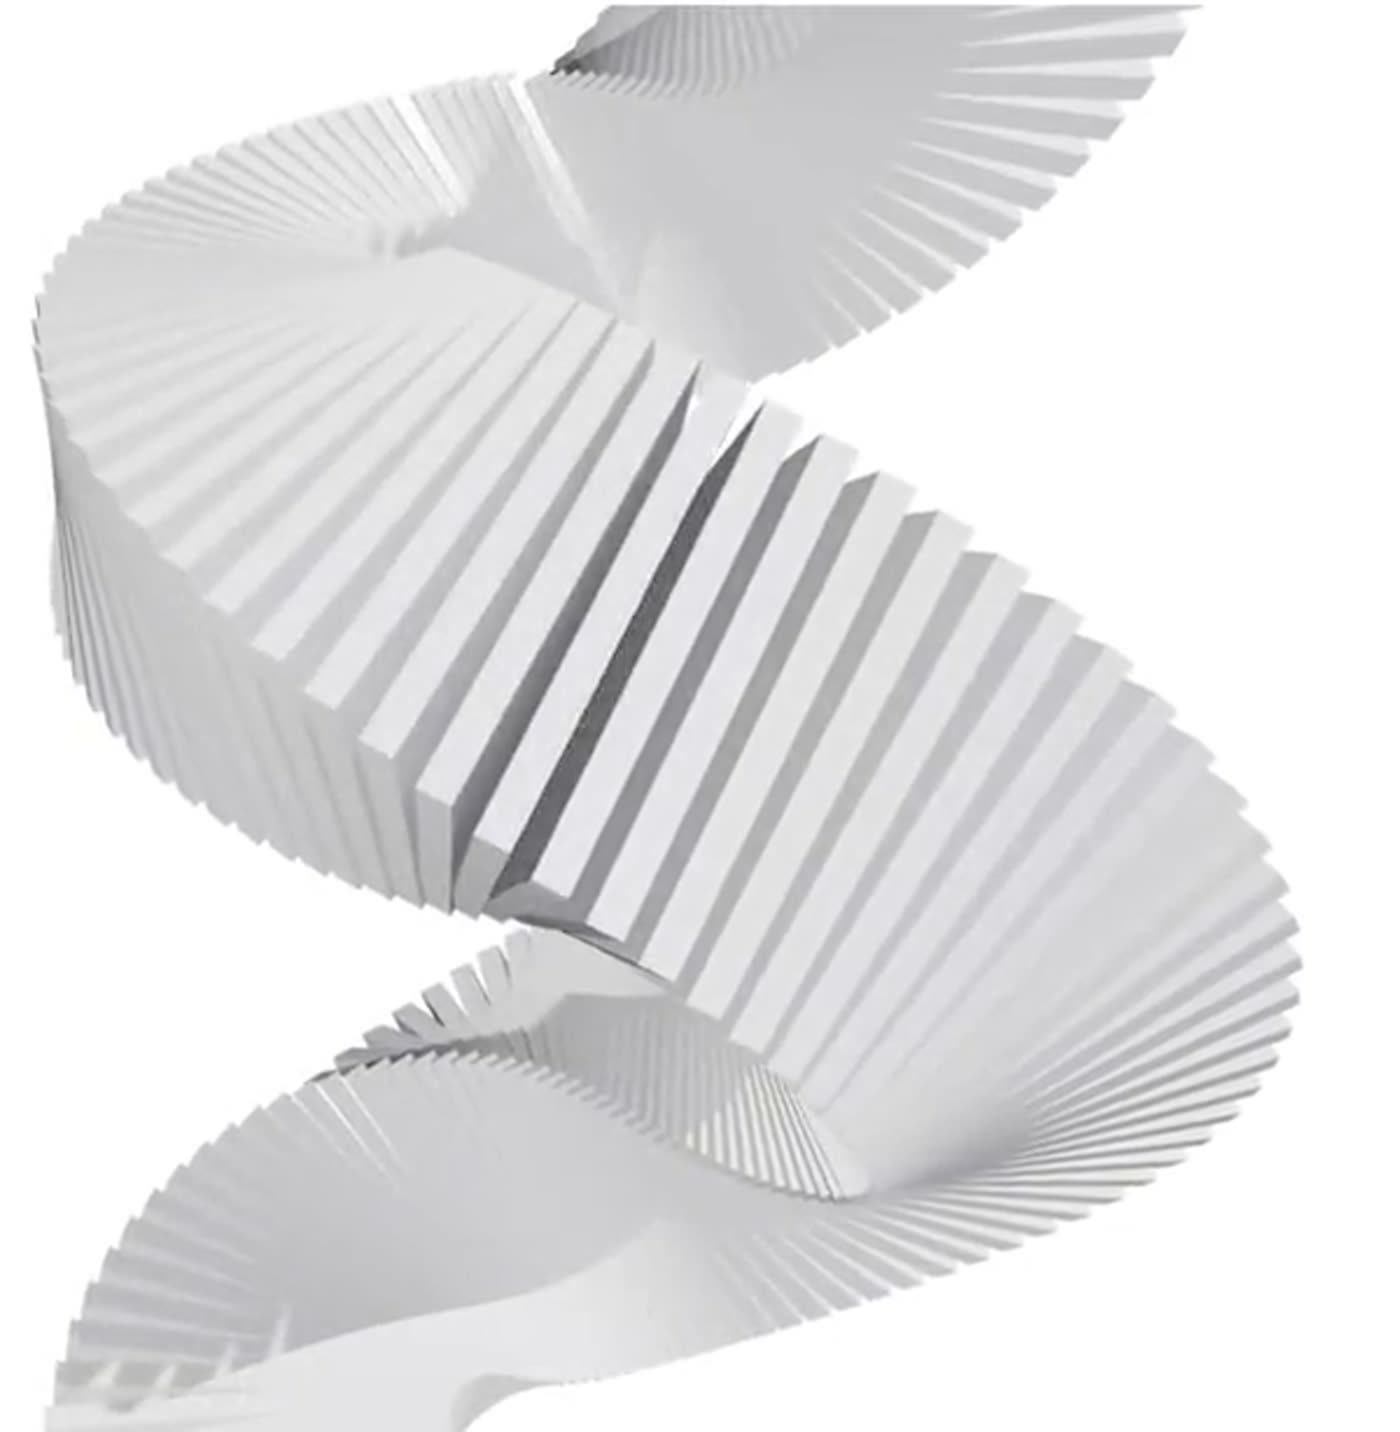
The six stages, and what runs in each.
Watch an event move from your devices to Mission Control. The labels under each stage are the parts that do the work.
- Step 1SidecarCollects logs inside your network and masks emails and card numbers by defaultOn-site collectorEmails and cards masked
- Step 2ParserReads every source into one standard formatUniversal Log ParserOCSF format
- Step 3iNTelligenceDetects, triages and reasons with on-cluster AIThree detectorsTriageOn-cluster AI
- Step 4ExAIExplains every verdict in plain wordsPlain-language verdictMITRE mapping
- Step 5FabricBlocks at your firewall once an analyst approvesAnalyst approvalFirewall block
- Step 6Mission ControlShows your team what needs attention nowG-ScoreCasesReports
Stages 1 and 2: collected and read on your site.
The Sidecar runs on a server inside your network. It receives logs from every device, reads each vendor's format into one standard, masks emails and card numbers by default and sends the events out over one outbound connection.
- No inbound firewall changes
- Device credentials stay on the collector
- Built-in device discovery and reachability checks
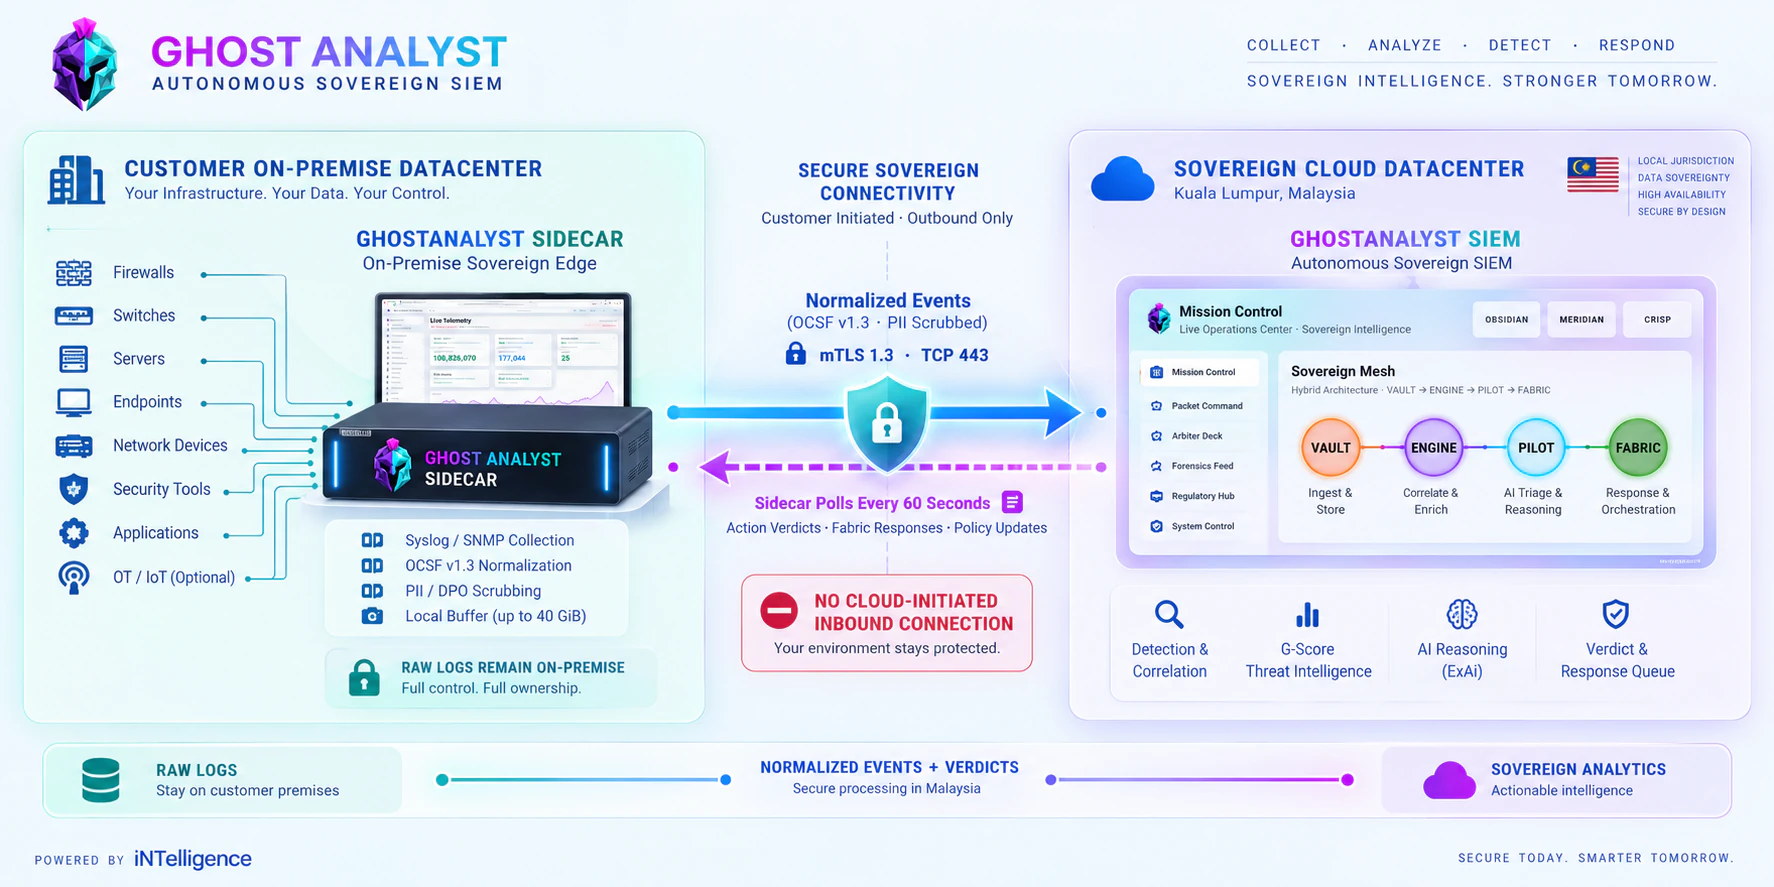
Stage 3: three ways of spotting an attack, run side by side.
Each detector looks for something different. An attack that hides from one method is still in view of the others.
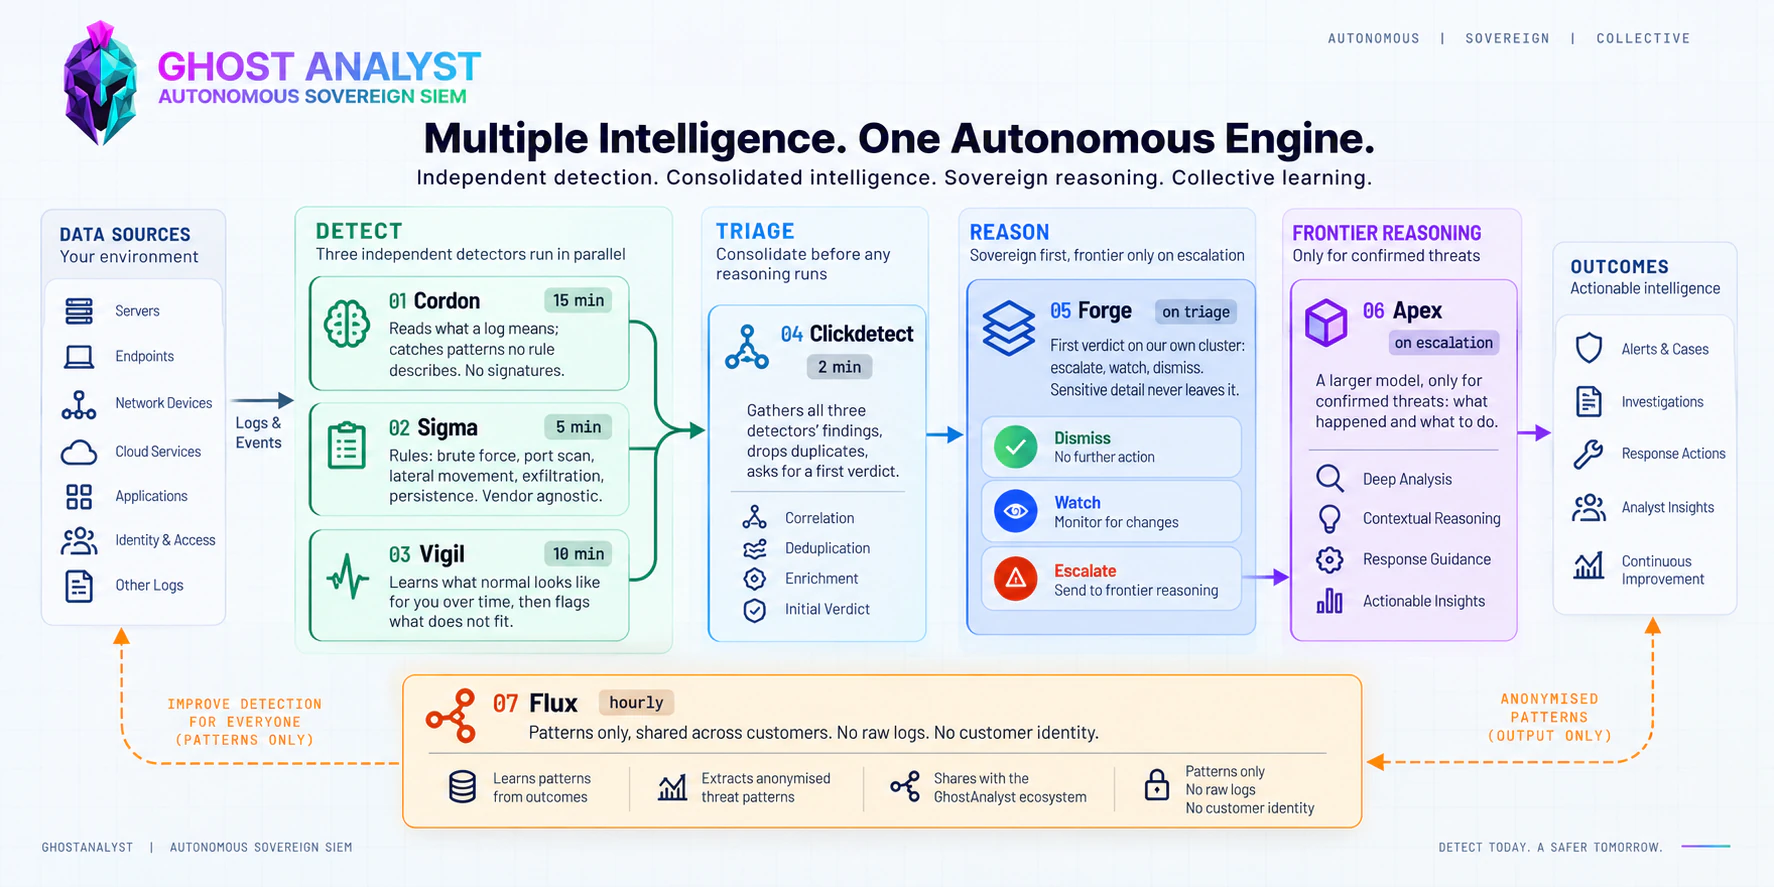
On-cluster AI writes the first verdict.
- First pass in your jurisdiction
An open-weight model on our own cluster decides: escalate, monitor or dismiss.
- Personal identifiers and secrets masked first
Only high-signal incidents get deeper reasoning from a hosted model. Before any of it is sent, an automatic filter masks the emails, IC, passport and phone numbers, MAC addresses and secrets it detects. Addresses and hostnames pass so the model can explain the alert. Masking is best effort, and if it fails, nothing is sent.
- Every verdict explained
Plain-language narrative, evidence trail and the MITRE ATT&CK technique it matches.
Stages 4 to 6: explained, approved, shown.
The case arrives with its reasoning. In Guided mode the agent can propose blocking an outside address at your firewall for a limited time, or a note to your on-call address, and each proposal cites the investigation steps it rests on. Nothing happens until an analyst approves, and a proposal nobody decides expires after an hour. Every workspace starts in audit mode, where the agent proposes nothing. Mission Control shows your whole network on one screen.
Explore Mission Control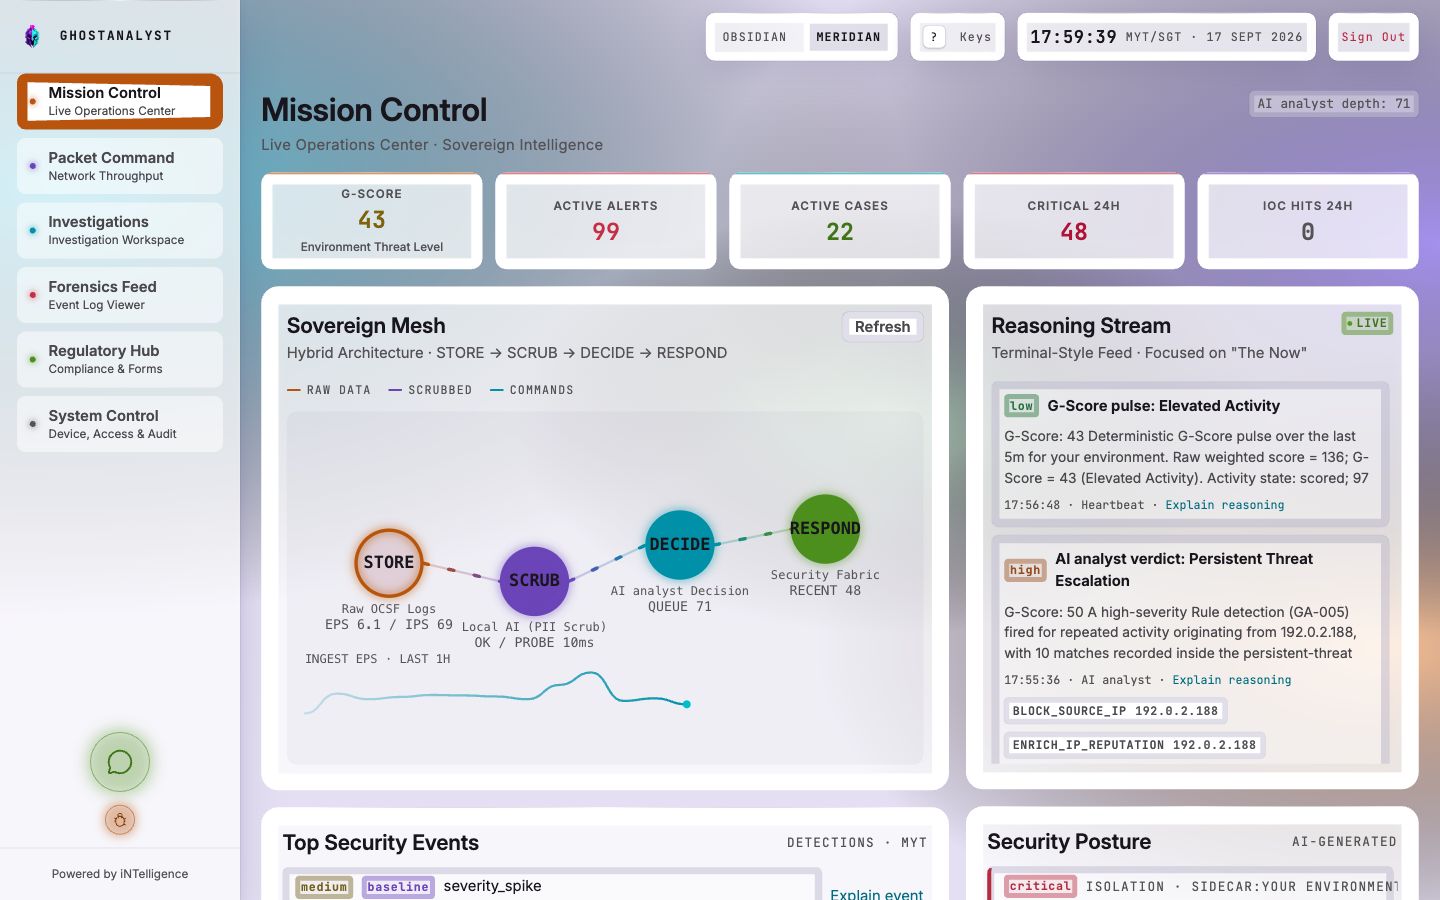
MITRE ATT&CK coverage, by tactic.
The 14 enterprise tactics in attack order, with the detection methods that look for each one.
- Reconnaissance
- Resource Development
- Initial Access
- Execution
- Persistence
- Privilege Escalation
- Defense Evasion
- Credential Access
- Discovery
- Lateral Movement
- Collection
- Command and Control
- Exfiltration
- Impact
This shows which methods look for each tactic. It is not a promise that every technique within a tactic is detected.
Watch the six stages run on your logs.
60-day full-platform trial. No credit card. No inbound firewall changes. Live in under an hour.