Catch the threats. Logs collected in your network, emails and card numbers masked by default.
GhostAnalyst reads your logs inside your own network, finds what matters, and hands your team a case with the reasoning attached. Your logs are collected inside your network, and emails and card numbers are masked by default before they reach your GhostAnalyst workspace.
Built with our technology partners · reads 300+ sources


Most SIEMs ask you to send your logs somewhere else first.
- Your data leaves your jurisdiction
Cloud SIEMs copy every raw log to someone else's servers, where foreign law can reach it.
- Your analysts drown in alerts
Thousands of detections a day, most of them noise, and no explanation for the ones that are not.
- Your bill grows with your logs
Pricing by data volume punishes you for collecting the evidence you need.
Six stages from raw log to a case your team can act on.
Collection and masking of emails and card numbers happen on your site. Everything after works on structured events.
- Step 1SidecarCollects logs inside your network and masks emails and card numbers by default
- Step 2ParserReads every source into one standard format
- Step 3iNTelligenceDetects, triages and reasons with on-cluster AI
- Step 4ExAIExplains every verdict in plain words
- Step 5FabricBlocks at your firewall once an analyst approves
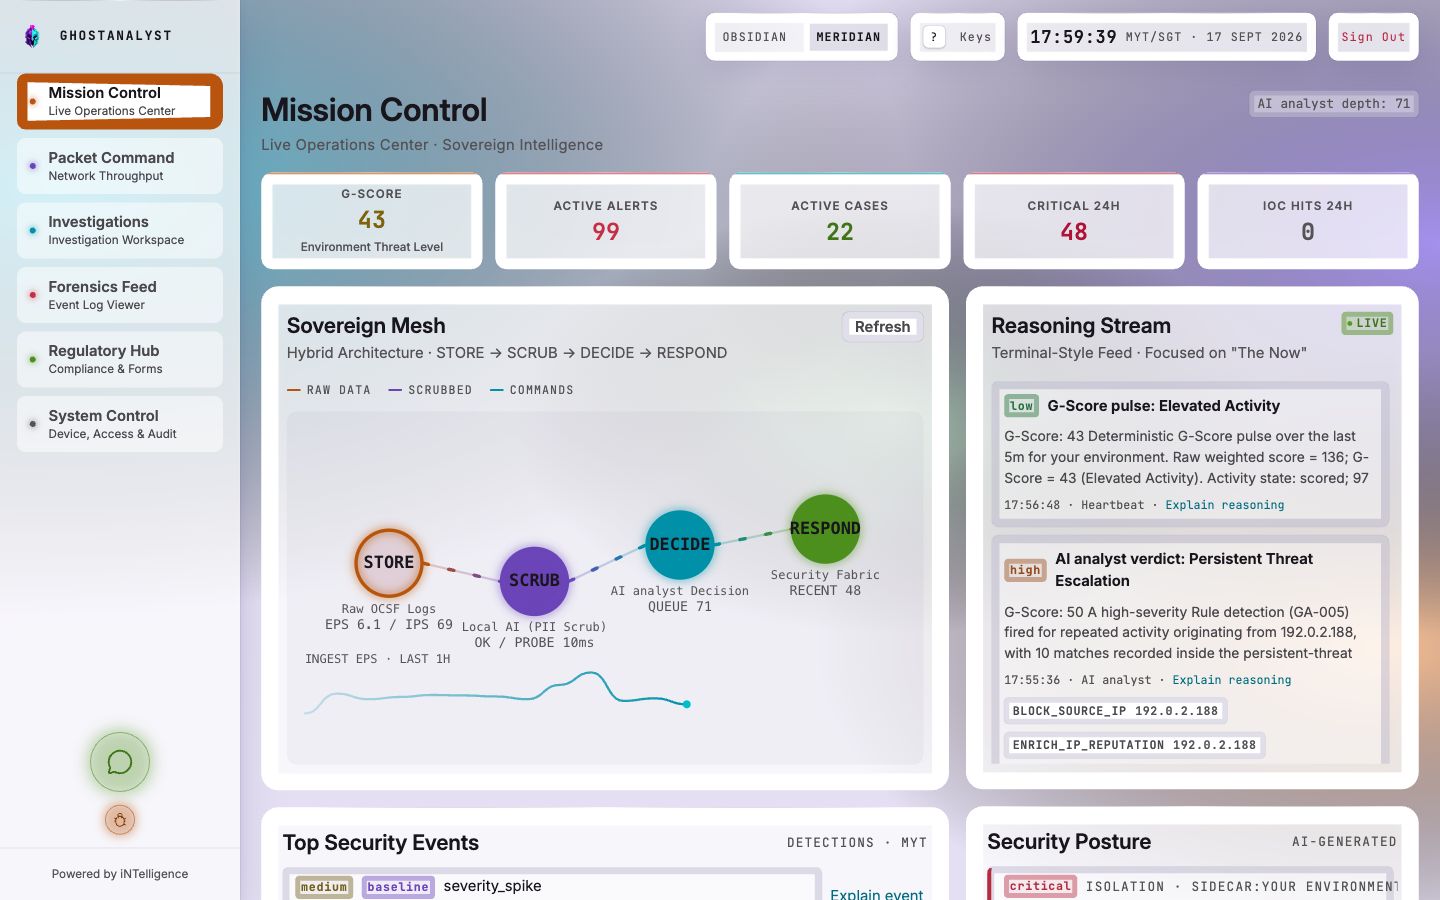
- Step 6Mission ControlShows your team what needs attention now
One screen for your whole network.
Mission Control shows your threat level, open cases and the reasoning behind every verdict, live.
- One G-Score for your whole environment, in five bands
- Every verdict explained in plain words
- The agent proposes a firewall block or an on-call note; nothing runs until an analyst approves
How we compare to Splunk, Sentinel and QRadar.
Out-of-the-box behaviour. Add-ons and separate products can extend what the others do.
| Capability | GhostAnalyst | Splunk | Sentinel | QRadar |
|---|---|---|---|---|
| Emails and card numbers masked by default before logs reach the cloud1 | Yes | Not natively | Not natively | Partial |
| On-cluster AI processing2 | Yes | Not natively | Not natively | Limited |
| Live in under an hour3 | Yes | Not typical | Not typical | Not typical |
| Built-in network monitoring4 | Yes | Not natively | Not natively | Not natively |
- Default deployment of each product as documented by its vendor. GhostAnalyst masking is on by default and can be turned off. QRadar offers an on-premises edition.
- Where the built-in AI features run by default, per vendor documentation.
- Time from installer to first detections on a standard deployment; others vary with scope and services.
- Network node monitoring included in the base product, without a separate tool.
Real numbers from a production deployment, not a demo.
- Sector
- Public service · regulated jurisdiction
- Deployment
- Live in under an hour; the team worked real cases from the first day
Your jurisdiction. Your rules.
Collection stays on your site, and you choose how far the AI reaches.
Collect on site, analyse in our private cloud
The Sidecar collects and cleans logs in your network. Analysis runs in our dedicated cloud region.
Mask before any hosted model
Only masked excerpts reach a hosted model. If masking fails, nothing is sent.
A licensed SOC behind the software.
NACSA licensedEvery subscription includes SOC and MDR: detection, validation, escalation and response, on-site included. Standard covers critical and high around the clock. Premium covers every severity, faster.
See it on your own logs.
60-day full-platform trial. No credit card. No inbound firewall changes. Live in under an hour.